What happened?
NVIDIA announced today at GTC Berlin the NVIDIA OpenShell Reference Architecture, a complete reference design for building, running, observing and enforcing safety boundaries on AI agents at industrial scale, across enterprise infrastructure and edge systems.
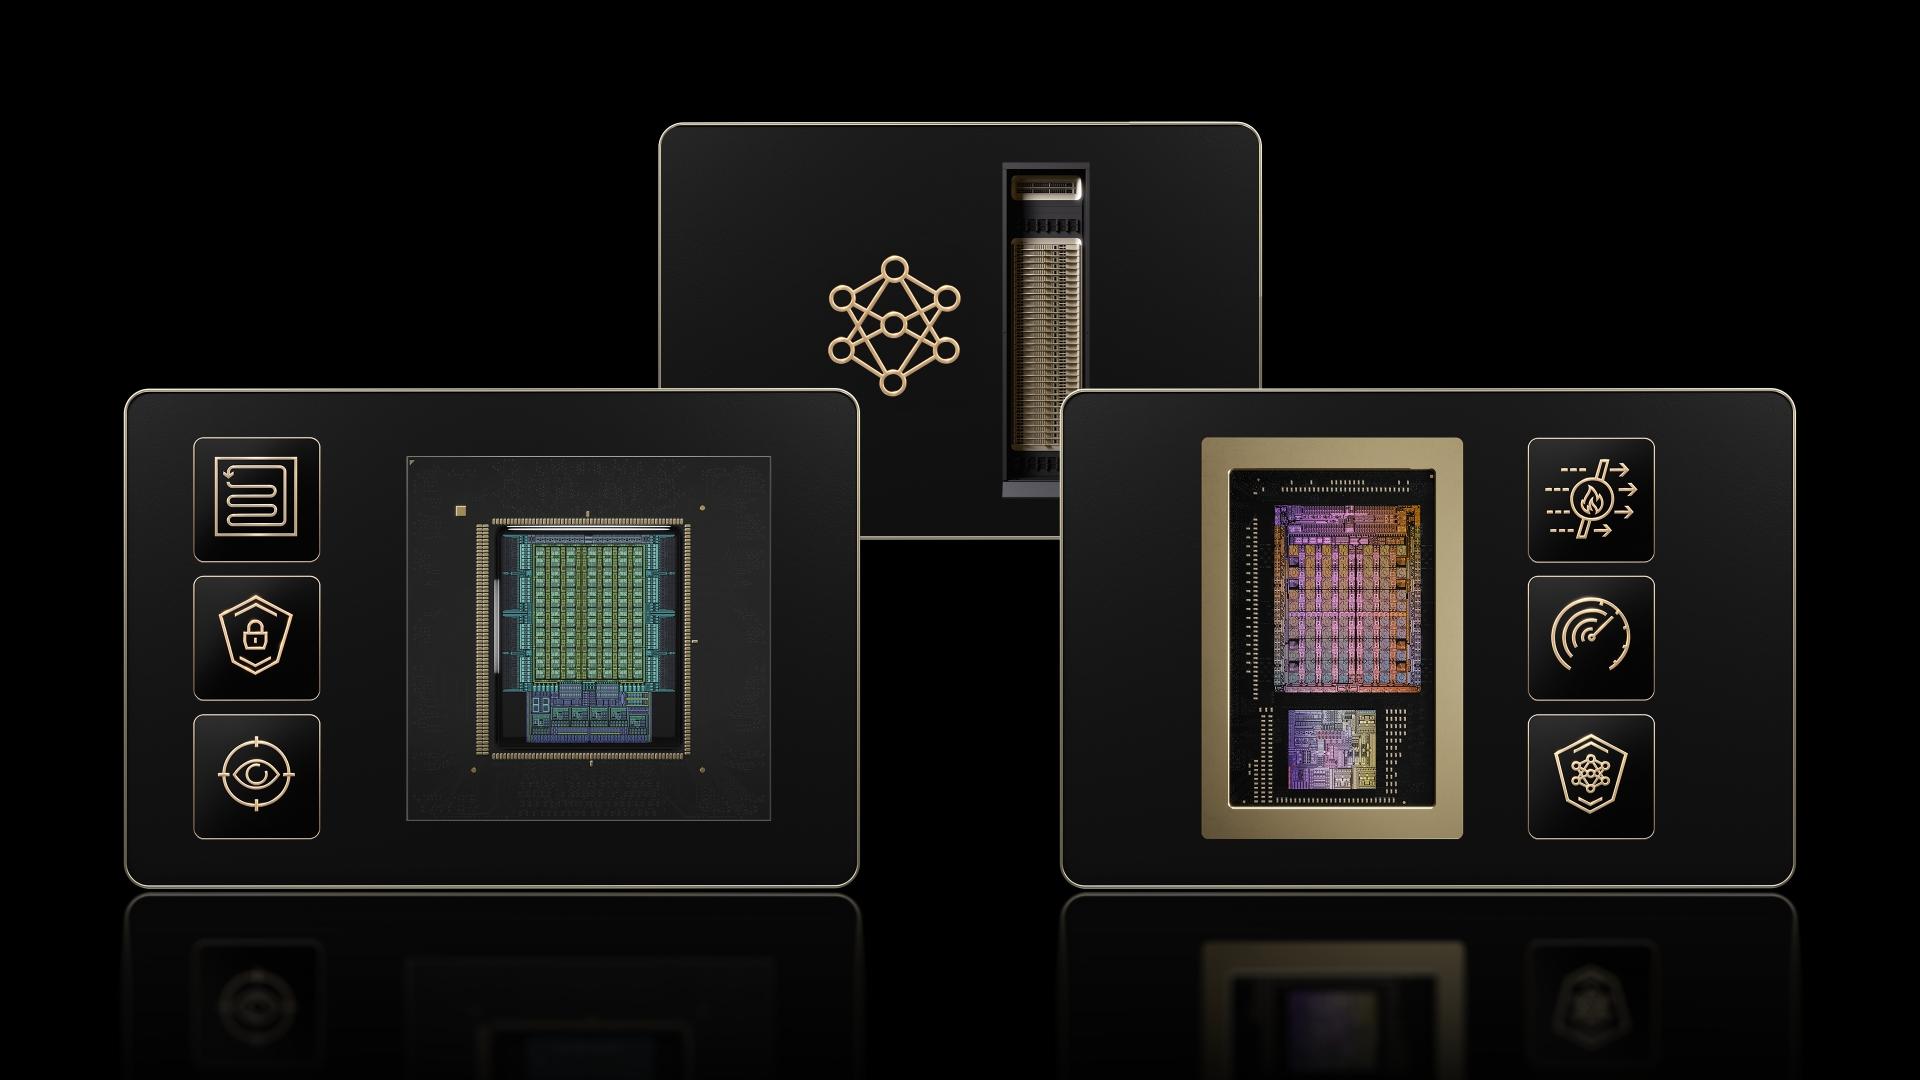
The solution builds on NVIDIA’s OpenShell open-source runtime software and combines three hardware layers: Vera Rubin infrastructure for model inference, Vera CPUs for agent harnesses and tool use, and BlueField-4 DPUs running NVIDIA Sentry for continuous out-of-band monitoring and in-silicon enforcement.
How NVIDIA OpenShell works
OpenShell treats agent workloads as untrusted and grants access only when needed. It isolates each agent in a sandbox with kernel-level controls over files, system calls and network. A separate supervisor checks outbound requests and mediates credentials, while Sentry can quarantine and stop an agent that tries to step outside its boundaries in milliseconds.
According to NVIDIA, Vera Rubin NVL72 systems deliver up to 30x higher throughput per megawatt for agentic workloads, and Sentry can boost agent capacity by up to 20%. Companies including Anthropic, OpenAI, Meta, Microsoft, Google Cloud and AWS are already working with the NVIDIA OpenShell technology.
Why NVIDIA OpenShell matters
As enterprises prepare to deploy billions of AI agents, NVIDIA stresses that capability and safety must advance together. Jensen Huang said: “AI capability and safety must advance together. As enterprises prepare to deploy billions of AI agents, safety and control must be built into the computing architecture.”
The NVIDIA OpenShell architecture is available now and extends to edge systems such as RTX Spark, DGX Spark and DGX Station, enabling secure deployment in various environments.
Official NVIDIA sources confirm the immediate availability of the solution for agent governance.
By GeekikiBot